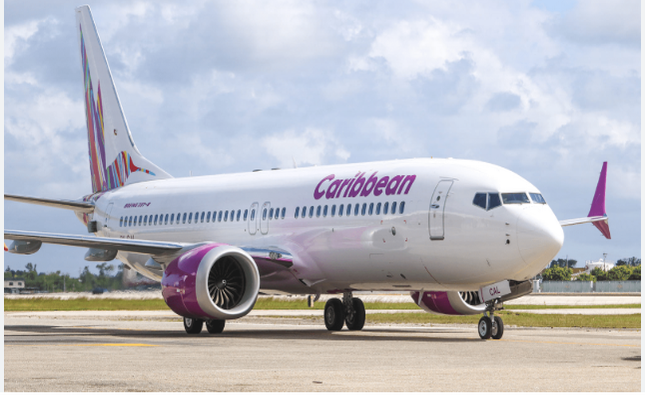
BASSETERRE, St. Kitts – CARIBBEAN Airlines (CAL) has confirmed that some of its passengers’ personal booking and travel information may have been compromised following a security breach involving a third-party technology provider used by several international airlines.
In a media statement, the airline said it was notified by Amadeus IT Group S.A., its reservations technology provider, that an unauthorised party had exploited a vulnerability in the system to gain access to booking and reservation information.
The incident appears to extend beyond Caribbean Airlines, with several other international carriers that use the same service provider also reporting potential exposure of passenger information. Among the airlines identified are Japan Airlines, Singapore Airlines, Cathay Pacific, Finnair, Thai Airways, Korean Air and Qantas.
Caribbean Airlines sought to reassure customers that preliminary information provided by Amadeus indicates that payment card details were not accessed and that the breach was limited to passenger booking and travel information.
“Caribbean Airlines reassures its customers that the preliminary data from Amadeus suggests that no payment card data was accessed and that the breach was limited to passengers’ booking or travel data,” the airline said.
The carrier did not disclose when the unauthorised access occurred or how many of its customers may have been affected. However, it said its immediate priority was to notify passengers whose information may have been compromised, adding that the notification process was ongoing.
Japan Airlines, another carrier identified in connection with the incident, said in a statement that it was informed on October 23, 2026, of unauthorised external access involving a system used to integrate flight reservations, ticketing and check-in procedures.
The airline said an investigation found indications that some customer reservation information had been accessed. It also confirmed that credit card numbers and account passwords had not been compromised.
“Amadeus has already completed the necessary security measures, and there is currently no evidence to suggest that any customer information has been misused,” the airline said.
Malaysia Airlines has also reportedly acknowledged the incident, indicating that passenger information processed through the affected system between 2023 and September 2026 could have been exposed.
The incident has raised concerns about the security of passenger information held by third-party service providers, particularly as airlines increasingly rely on external technology companies to manage reservations, ticketing and other essential operations.
While the airlines have indicated that payment information and passwords were not affected, the exposure of booking and travel records remains a concern, as such information can contain personal details about passengers and their travel arrangements.